

Your builders say the appliance is prepared. Your automated safety scans present no important findings. An AI coding assistant has reviewed the code.
Then an enterprise buyer asks for a penetration check. An investor requests technical due diligence. One other advisor recommends a code audit.
Are these completely different names for a similar service? Do you want all three? And what would you be paying somebody to find that your instruments haven’t already discovered?
A founder on Reddit raised virtually precisely this concern after constructing an AI-assisted net platform: how a lot can automated scanners detect, how a lot ought to they belief AI assessment, and when does paying for a safety audit or penetration check turn out to be worthwhile? The query displays a buying downside, not only a technical one.
The suitable evaluation will depend on the choice it’s essential make and the proof you might be lacking.
Don’t begin with “Which audit bundle ought to we purchase?”
Begin with: “What do we have to know earlier than we launch, signal this buyer, approve this funding, or rebuild this product?”
What Is the Distinction Between a Code Audit, Penetration Check, and Technical Due Diligence?
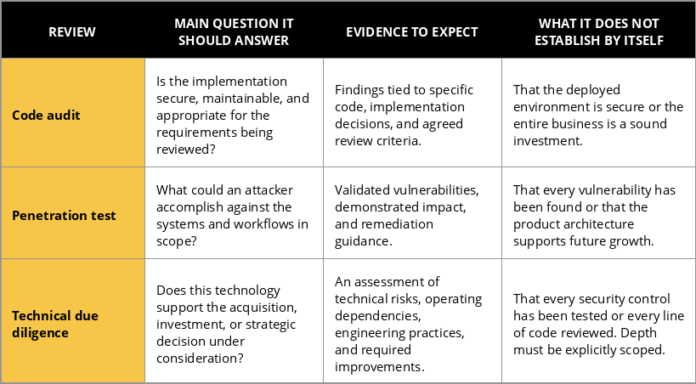
A code audit examines the implementation of software program. A penetration check investigates how an utility or system will be compromised inside a licensed scope. Technical due diligence evaluates whether or not the know-how, engineering capabilities, and related dangers assist a enterprise resolution. Their strategies can overlap, however their aims are completely different.

A technical due diligence engagement would possibly embrace a code audit and suggest focused penetration testing. A penetration tester would possibly use supply code to analyze a suspected weak point. These are complementary strategies, not essentially three separate purchases.
Purchase the required investigation, not the most important assortment of service labels.
Do You Nonetheless Want a Safety Audit After AI Code Evaluation and Automated Scanning?
Not robotically. However a clear scan will not be adequate proof that your utility is safe.
Automated static evaluation helps establish potential vulnerabilities in supply code. Its limitations embrace false positives, missed vulnerabilities, and incomplete visibility into exterior techniques or runtime configuration. OWASP describes these instruments as helpful aids to evaluation, fairly than full substitutes for it.
AI assessment additionally requires validation. GitHub’s documentation states that Copilot code assessment can miss issues, establish issues that don’t exist, and counsel incorrect or insecure adjustments. GitHub recommends utilizing it to complement human assessment, not change it.
The buying query is subsequently not:
“Can a human discover one thing an AI software missed?”
It’s:
“What is going to this evaluation confirm that our current course of has not verified?”
A Clear Scan Can Nonetheless Go away a Enterprise-Essential Query Unanswered
Contemplate an illustrative B2B utility that enables prospects to export account information.
The export endpoint could use parameterized database queries. The person could also be authenticated. The applying could cross its current exams.
Nevertheless, does the export course of confirm that the requested data belong to that person’s group? Does the background job protect that restriction? Can somebody whose entry was revoked nonetheless retrieve a beforehand generated export?
These are questions concerning the utility’s meant guidelines and their implementation throughout a workflow. OWASP’s business-logic steering explains why safety issues can exist even when particular person inputs and capabilities seem technically legitimate.
A worthwhile evaluation ought to examine these particular uncertainties.
A further reviewer will not be precious just because they’re human or exterior. Ask how their strategies, entry, experience, and proof will add to what you have already got.
When Is a Code Audit Value Paying For?
A code audit is value contemplating when uncertainty concerning the implementation is obstructing a launch, creating recurring issues, or influencing a big improvement resolution.
The time period “code audit” is broad. Earlier than requesting proposals, specify whether or not you want a security-focused supply code assessment, a maintainability evaluation, an structure assessment, or a mix.
A report about naming conventions and duplicated capabilities will not be an sufficient reply to a query about unauthorized customer-data entry.
When You Must Confirm Safety-Delicate Implementation
A safety code audit ought to work from outlined necessities fairly than a normal instruction to “search for vulnerabilities.”
For a customer-facing utility, request protection applicable to its authentication, authorization, session administration, sensitive-data dealing with, and different related controls. OWASP’s Utility Safety Verification Customary, or ASVS, gives a structured basis for specifying application-security necessities.
Ask the reviewer to attach findings to the related implementation and clarify the situations beneath which the issue issues.
“Authorization might be improved” will not be actionable.
“Background exports don’t constantly implement the identical account restrictions as interactive requests” is a discovering your engineering group can examine and resolve.
That instance is illustrative, not a declare a couple of specific product.
When You Are Deciding Whether or not to Rebuild or Refactor
For a rebuild resolution, outline a distinct goal.
Ask the evaluation to differentiate between structural constraints and localized issues. Require proof for why the prevailing system can’t meet the proposed necessities, fairly than accepting “legacy code” or “technical debt” as adequate justification.
The deliverable ought to evaluate sensible choices: stabilize the present system, change chosen parts, modernize incrementally, or rebuild.
A helpful advice must also acknowledge uncertainty. A repository assessment alone shouldn’t be introduced as proof {that a} alternative system shall be cheaper or quicker.
What to Specify within the Code Audit Scope
Request a named repository, department or commit, the modules being reviewed, the assessment standards, and the depth of investigation.
Make clear whether or not the assessor will run the appliance, look at deployment configuration, and validate findings in a check setting.
This distinction issues as a result of supply code assessment has limits: runtime habits could also be troublesome to evaluate, and the code reviewed could not match what’s deployed.
A focused assessment will be precious. A focused assessment introduced as full protection will not be.
Penetration Check vs. Vulnerability Evaluation: What Are You Paying For?
A vulnerability evaluation identifies and evaluates potential weaknesses. A penetration check goes additional by investigating exploitability and the results of weaknesses inside an agreed scope.
The excellence will not be merely “automated versus guide.” Instruments can assist penetration testing. The extra worth is the investigation: reasoning about workflows, validating findings, and figuring out whether or not weaknesses can mix right into a significant assault path.
When Penetration Testing Is the Proper Buy
Contemplate penetration testing when your unresolved query issues the habits of a operating system.
For instance:
“Can a normal person entry administrative performance?”
“Can one buyer attain one other buyer’s info?”
“Can an uncovered integration be abused to carry out an unauthorized motion?”
These correspond to areas reminiscent of authorization, privilege escalation, session dealing with, and business-logic testing coated by OWASP’s Internet Safety Testing Information.
For a B2B utility, ask whether or not testing will embrace lifelike person roles and buyer boundaries. An evaluation restricted to unauthenticated public pages can’t reply questions on authenticated workflows it by no means examines.
Does a Penetration Tester Want Supply Code?
Not all the time.
A check can start with restricted information of the system, with chosen documentation and accounts, or with intensive entry to implementation particulars. Offering supply code can assist the tester examine habits and validate suspected points extra effectively. OWASP recommends combining testing strategies fairly than counting on a single view of the appliance.
Don’t withhold helpful info merely to make the train appear extra lifelike. First resolve whether or not the target is to simulate a specific attacker or to maximise the invention of necessary weaknesses throughout the accessible time.
What a Penetration Check Can not Promise
A penetration check is bounded by its scope, entry, time, and testing situations. OWASP’s reporting steering explicitly acknowledges these limitations and warns towards treating a point-in-time evaluation as a guaranty that each safety concern has been recognized.
Earlier than work begins, require written authorization, agreed targets, prohibited actions, test-data dealing with, escalation contacts, and stopping situations. Affirm permission for any third-party techniques concerned.
You might be buying managed safety investigation, not unrestricted permission to disrupt manufacturing.
When Do You Want Technical Due Diligence As an alternative of a Safety Audit?
Technical due diligence is the extra applicable place to begin when the choice is broader than whether or not the appliance comprises exploitable vulnerabilities.
An acquisition purchaser wants to know what they’re inheriting. A board could have to assess whether or not an engineering group can execute its roadmap. A founder getting ready for funding might have an unbiased view of know-how dangers and lacking proof.
Purchase.com’s steering for software-business sellers illustrates this broader scope by way of improvement practices, source-control historical past, safety processes, dependencies, and reliability.
A Safe Utility Can Nonetheless Be Tough to Function or Scale
For an acquisition or main funding, ask the assessment to analyze questions reminiscent of:
Can one other group deploy and function the product with out the founder?
What assumptions assist the expansion plan?
Which exterior suppliers are important to service supply?
How a lot of the roadmap will depend on unverified engineering estimates?
What proof helps restoration, reliability, and maintainability claims?
These questions require greater than a vulnerability report. They require examination of the connection between the know-how and the proposed marketing strategy.
The place software program licensing, possession, or contractual rights are materials, request the related technical proof and coordinate the conclusions with authorized counsel. Possession of a repository shouldn’t be handled as an entire possession dedication.
Insist on Proof Behind the Technical Due Diligence Report
For every materials conclusion, ask the assessor to differentiate:
Verified proof, reminiscent of noticed deployment habits.
Administration statements, reminiscent of a claimed capability restrict.
Estimates, such because the possible effort to exchange a element.
Unresolved questions, reminiscent of entry that was not supplied.
That is particularly necessary when time is restricted.
Don’t settle for “the system is scalable” with out asking what workload, setting, and proof assist that conclusion. When efficiency is materials to the choice, explicitly scope applicable testing fairly than assuming it’s included.
Does an AI Product Want a Totally different Safety Audit?
First, distinguish an AI-built utility from an AI-powered utility.
An AI-built utility could have been developed utilizing coding assistants however comprise no AI performance. An AI-powered utility could course of prompts, retrieve paperwork, invoke fashions, or enable brokers to take actions.
The second class introduces further evaluation necessities.
For instance, OWASP identifies immediate injection as a threat through which inputs affect mannequin habits in unintended methods. Its steering additionally notes that retrieval-augmented technology and fine-tuning don’t totally eradicate this threat.
OWASP individually identifies extreme company: damaging actions enabled by extreme performance, permissions, or autonomy granted to an AI system.
For an AI-powered product, explicitly scope questions on retrieved content material, information entry, software permissions, approval boundaries, and unauthorized actions.
Additionally distinguish AI safety testing from AI product analysis. Request separate proof for job accuracy, acceptable failure habits, working prices, and dependence on mannequin suppliers. A check of entry controls shouldn’t be introduced as proof that the product offers dependable solutions.
Which Evaluation Ought to You Purchase First?
Use the next as a buying framework, not a common sequence.

The target is to not purchase each service.
It’s to keep away from making a consequential resolution with the fallacious sort of proof.
When Is It Cheap To not Purchase a Giant Exterior Audit?
Exterior spending ought to handle an outlined hole.
Earlier than buying a broad assessment, ask whether or not your group already has the experience, time, entry, and independence wanted to reply the related questions. Additionally contemplate whether or not a buyer or different stakeholder requires exterior proof.
An remoted prototype utilizing artificial information could justify a distinct evaluation scope from a dwell platform dealing with delicate buyer info. That may be a cause to dimension the work appropriately, to not assume that safety not issues.
There may be additionally no smart rule that safety assessment turns into vital solely after reaching a specific income stage.
Base the choice on publicity, penalties, uncertainty, and proof necessities, not merely firm dimension.
A targeted assessment would be the proper buy. In one other scenario, enhancing the inner verification course of could also be extra helpful than commissioning one other report.
What Ought to a Paid Evaluation Report Truly Give You?
The report ought to assist executives decide and engineers take motion. OWASP’s reporting steering emphasizes each audiences, together with scope, limitations, enterprise affect, and the data wanted to know and resolve findings.
Require 4 clear outputs.
A choice abstract. What does the proof indicate for the proposed launch, buy, buyer dedication, or improvement plan? Which choices stay conditional?
Proof-backed findings. What was noticed, the place was it noticed, beneath what situations, and what’s the sensible consequence? Distinguish a confirmed concern from a chance that wants extra investigation.
Seen protection and limitations. Which techniques and variations had been examined? Which roles or workflows had been excluded? What couldn’t be verified as a result of entry or performance was unavailable?
A prioritized response. What ought to be mounted, investigated additional, scheduled, or explicitly accepted by the accountable enterprise proprietor? How will accomplished fixes be verified?
An extended report will not be inherently a helpful report.
“Not examined” should stay completely different from “examined with no discovering.”
After remediation, incorporate related checks into the event course of. NIST’s Safe Software program Improvement Framework emphasizes lowering vulnerabilities, addressing their root causes, and stopping recurrence throughout the software program lifecycle.
The target is to not buy the identical discovery repeatedly.
Not sure whether or not your product wants a code audit, penetration check, or technical due diligence?
ISHIR helps you establish technical dangers and prioritize the subsequent steps earlier than you commit.
Ceaselessly Requested Questions About Code Audits and Technical Due Diligence
Q. Is a code audit the identical as a safety audit?
No. A code audit can handle safety, maintainability, implementation high quality, or different agreed issues. A safety evaluation might also look at operating techniques and operational controls. Ask for the precise scope and strategies fairly than counting on both label.
Q. Do I would like a penetration check after a code audit?
Probably, relying on the remaining uncertainty. Code assessment and testing of a operating utility present completely different views. Use penetration testing to analyze related deployed habits and validate safety dangers that the code assessment alone can’t resolve.
Q. Can technical due diligence be carried out with out source-code entry?
A restricted evaluation can nonetheless look at structure paperwork, demonstrations, operational proof, and engineering practices. Nevertheless, it shouldn’t make unsupported claims about implementation it has not inspected. For a cloth transaction, specify what conclusions stay provisional till the mandatory entry is supplied.
Q. How typically ought to we repeat a safety assessment?
Set the cadence round threat, important adjustments, and relevant stakeholder necessities. Necessary releases could justify focused reassessment fairly than ready for a calendar anniversary. OWASP’s DevSecOps steering acknowledges the restrictions of relying completely on an annual penetration check when software program adjustments between engagements.
Q. Does a SOC 2 report change penetration testing?
No. A SOC 2 examination and a penetration check have completely different aims and proof necessities. Decide what the SOC 2 report covers and which application-security questions stay unanswered fairly than assuming one replaces the opposite.
Q. What’s the greatest evaluation for a startup with a restricted price range?
Begin with probably the most consequential unresolved query. Request a clearly bounded evaluation of the related workflow, system, or transaction threat. Protect the excellence between a restricted assessment and broader assurance, and reserve sources to resolve and confirm the findings.
Pay for Proof That Modifications the Determination
The most cost effective evaluation is poor worth when it solutions the fallacious query. Essentially the most intensive evaluation is pointless when a smaller investigation would resolve the choice.
A code audit can make clear implementation threat. A penetration check can set up what an attacker might accomplish inside scope. Technical due diligence can join know-how proof to a broader enterprise resolution.
The assessment value paying for is the one which replaces a cloth assumption with proof you possibly can act on.
How ISHIR Helps
ISHIR’s technical due diligence providers assess software program, SaaS platforms, cloud techniques, and AI-enabled merchandise, with consideration to know-how threat, safety publicity, scalability, and execution readiness. The service is designed to assist funding, acquisition, and strategic know-how choices.
Begin with the choice your group must make. Outline the required proof, agree on the evaluation boundaries, and establish the place specialist testing is important.

