

Your workforce desires an AI agent to elucidate income modifications, examine help points, or summarize operational exceptions utilizing Snowflake information.
The connection works. The agent produces helpful solutions. Then somebody asks the query that ought to have come earlier than the demo:
“Precisely what else can this agent entry?”
That query isn’t resistance to AI adoption. It’s a production-readiness requirement.
Think about a help agent that wants subscription standing and up to date help tickets. It doesn’t want payroll data, unrestricted buyer exports, or permission to vary database objects. Connecting it via an engineer’s on a regular basis account could also be handy, however comfort isn’t an authorization mannequin.
To attach AI brokers to Snowflake safely, authorize the precise workflow reasonably than the one that configured the mixing. Use a restricted id or delegated session, constrain lively roles, expose solely mandatory instruments and information, handle credentials outdoors the mannequin, and check that prohibited actions really fail.
The vital distinction is between an agent that has been instructed to not entry one thing and an agent that can’t entry it.
Why Can a Snowflake AI Agent Entry Extra Than Its Assigned Function Suggests?
As a result of deciding on a major function doesn’t at all times describe the session’s full authorization context.
Snowflake can authorize operations utilizing privileges from lively major and secondary roles, together with inherited roles. The PUBLIC function can also be routinely out there to each person and function. Direct grants to customers can matter when secondary roles are set to ALL. A task named AI_READER is due to this fact not adequate proof that the connection is restricted.
The sensible lesson is easy:
Examine efficient entry via the precise integration. Don’t approve manufacturing entry primarily based on a connection file, a job identify, or a profitable demonstration.
Begin by answering three questions: Which id reaches Snowflake? Which roles and insurance policies are lively? Which privileges do the invoked instruments use?
These solutions decide the safety boundary.
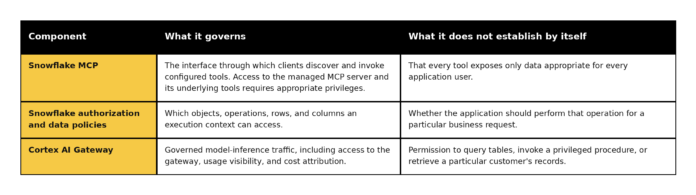
Snowflake MCP vs. Cortex AI Gateway: Which One Controls Entry?
Snowflake MCP and Cortex AI Gateway clear up totally different issues. Treating both as an entire safety resolution leaves gaps. 
How one can Construct a Least-Privilege Snowflake AI Integration
1. Determine Whether or not the Agent Acts for a Consumer or for Itself
These are totally different id fashions.
A delegated agent acts on behalf of a specific particular person. An autonomous agent performs an outlined workload underneath its personal id. Snowflake’s present agent-identity documentation distinguishes these fashions and helps agent-aware identification via managed entry factors and appropriately configured OAuth integrations.
For an employee-facing assistant, protect the requesting person’s id and apply software authorization earlier than invoking instruments. A shared, broadly privileged backend account mustn’t change into a shortcut round employee-level restrictions.
For an autonomous workflow, create a devoted id with solely the workload’s required entry. Snowflake paperwork the SERVICE_AGENT person sort for automated AI brokers working underneath their very own id and privileges. It helps non-interactive authentication strategies, together with workload id federation, key-pair authentication, and programmatic entry tokens. Verify help within the chosen consumer and endpoint.
For customer-facing purposes, resolve tenant and buyer authorization from the authenticated software session. Don’t let the mannequin provide an unrestricted tenant identifier and deal with it as proof of entry.
Identification ought to come from a trusted authentication path, not from the immediate.
2. Limit the Session, Not Simply the Default Function
For a narrowly scoped Snowflake OAuth integration, use an specific function allowlist and disable pointless secondary-role activation.
Related Snowflake OAuth settings embrace ALLOWED_ROLES_LIST and OAUTH_USE_SECONDARY_ROLES = NONE. The documentation specifies that the allowlist can’t be mixed with OAUTH_USE_SECONDARY_ROLES = IMPLICIT. Hold function switching disabled except the workflow genuinely requires it. Exterior OAuth has its personal configuration, so don’t assume an identical settings apply.
Additionally confirm what the MCP consumer really requests. Some purchasers use a scope that leads to the person’s default function reasonably than the function the workforce anticipated.
For a connector-based integration, a startup assertion akin to USE SECONDARY ROLES NONE can set up an preliminary session state. It isn’t an entire boundary if the id can subsequently activate broader roles. Limit the underlying grants and permitted session conduct.
3. Grant Entry to Accredited Knowledge, Not Complete Databases
Begin with the smallest helpful information product.
For a help workflow, that is perhaps a reviewed view containing subscription standing, plan info, and related help historical past. Exclude fields that don’t contribute to the duty.
4. Construct an Audit Path That Can Clarify the Enterprise Request
A database question log alone isn’t the entire software audit.
Your investigation ought to be capable to join the authenticated requester, agent and software model, instrument name, authorization choice, Snowflake question identifier, execution outcome, and any approval.
Snowflake Question Historical past exposes particulars together with function, warehouse, question tag, execution standing, and error info. Use these data alongside software telemetry reasonably than treating the agent’s dialog transcript because the authoritative execution report.
Use application-controlled correlation identifiers to attach the data. Keep away from placing secrets and techniques or pointless private information into tags and logs.
5. Evaluate Each Device’s Execution Rights
“Learn-only” isn’t a single change that makes an agent protected.
It helps shield in opposition to modification. It doesn’t set up that the returned info is acceptable, that retrieval is tenant-isolated, or {that a} callable program can’t carry out extra actions.
How Do You Check {That a} Snowflake AI Agent Can not Exceed Its Permissions?
A profitable reply proves performance. It doesn’t show isolation.
Use a staging setting with consultant insurance policies and artificial delicate data. The next is a proposed acceptance suite, not a declare that ten assessments assure safety.

Run destructive assessments via each the agent interface and the underlying instrument boundary.
An agent saying “I can’t assist with that” isn’t adequate when the instrument beneath would nonetheless execute the request.
Embrace pooled connections, repeated requests, and credential renewal within the assessments. Reject deployment when id or tenant context can carry over incorrectly between requests
How ISHIR Helps You Safe Snowflake AI Agent Integrations
Your AI agent wants sufficient entry to resolve a enterprise drawback, not sufficient entry to create a bigger one.
ISHIR will help your workforce design, assessment, and strengthen Snowflake AI integrations round an outlined enterprise workflow. The main target is on making entry enforceable, testing permission boundaries, and giving your engineering and safety groups visibility into what the agent really does.
Not sure what your Snowflake AI agent can really entry?
Request a safe Snowflake agent-integration structure assessment with ISHIR to evaluate id, permissions, instrument boundaries, and auditability.
Incessantly Requested Questions
Q. Can I join an AI agent to Snowflake utilizing my current account?
Technically, an integration can use a human id, however its efficient session should be intentionally restricted. Don’t assume deciding on a lower-privilege function removes entry inherited via different lively roles. For user-facing workflows, use a managed delegated connection. For autonomous workloads, desire a devoted agent id with workload-specific permissions.
Q. Is a read-only Snowflake function sufficient to stop information leakage?
No. Learn-only entry addresses modification, not whether or not the id can learn an excessive amount of. Retrieval providers and proprietor’s-rights packages additionally require separate assessment. Restrict uncovered information, implement person authorization, and check what reaches the instrument outcome and mannequin context, not solely the ultimate reply.
Q. Does entry to a Snowflake MCP server routinely grant entry to its instruments?
No. The server and referenced instruments have separate entry necessities. Relying on the instrument, permissions could embrace entry to a Cortex Search service, a semantic view, a Cortex Agent, or a operate or saved process. Provision solely the sources the workflow wants.
Q. How do I cease an AI agent from inheriting secondary roles?
Use controls applicable to the authentication path. Snowflake OAuth helps proscribing permitted roles and secondary-role conduct. A task-restricted PAT doesn’t use secondary roles. For connector periods, disabling secondary roles at startup is just one layer; additionally prohibit the id’s grants and skill to activate broader entry.
Q. Does Cortex AI Gateway change Snowflake RBAC or MCP authorization?
No. Cortex AI Gateway governs inference site visitors routed via it. It doesn’t grant database privileges or change instrument authorization. Gateway entry additionally doesn’t take away the necessity for the underlying mannequin permissions. Design and check inference governance individually from information entry.

