

The technical due diligence report lands in your inbox.
There are 47 findings. Seven are marked important. Twelve are excessive precedence. Your structure wants work. Check protection is inconsistent. A number of dependencies are outdated. Cloud prices are rising. Documentation is incomplete. One senior engineer seems to grasp a business-critical subsystem higher than anybody else.
Your CEO asks the query the report itself could not reply:
“What can we truly repair first?”
That is the place many technical due diligence workouts lose worth. The evaluation identifies issues, however the group turns each discovering right into a backlog merchandise. Engineering begins fixing no matter seems technically ugly. Safety needs vulnerabilities first. Product refuses to delay the roadmap. Finance needs a remediation finances. The board needs to know whether or not the underlying expertise danger is below management.
An excellent technical due diligence remediation plan ought to resolve that battle.
The target is to not remove each imperfection within the codebase. It’s to find out which technical dangers can materially harm clients, income, safety, reliability, product supply, or the corporate’s development plan, then repair them in the appropriate sequence.
For SaaS firms, this distinction is particularly necessary. AWS’s SaaS Lens treats SaaS structure throughout operational excellence, safety, reliability, efficiency effectivity, value optimization, and sustainability. It additionally emphasizes that there isn’t a single structure applicable for each SaaS enterprise.
Which means the query after a technical due diligence of SaaS shouldn’t be:
“What’s fallacious with our expertise?”
It’s:
“Which findings threaten the enterprise consequence we are attempting to attain, and what’s the lowest-risk sequence for addressing them?”
What Is a Technical Due Diligence Remediation Plan?
A technical due diligence remediation plan converts the findings from a technical due diligence report into an executable expertise roadmap with priorities, dependencies, homeowners, effort estimates, acceptance standards, and enterprise influence.
It ought to reply 5 questions:
1. What requires rapid containment?
2. What foundational issues make different fixes unreliable?
3. What technical debt needs to be refactored somewhat than rebuilt?
4. What can safely be deferred or consciously accepted?
5. How will we show that every materials danger has truly been diminished?
That is totally different from copying findings into Jira.
A discovering tells you what was noticed. A remediation roadmap determines what ought to occur due to it.
That distinction is the place CTO judgment issues.
The Largest Mistake After Technical Due Diligence: Treating Each Discovering Equally
Think about a fictional B2B SaaS firm known as Northstar.
Northstar has grown rapidly from founder-built software program right into a platform serving enterprise clients. A technical due diligence evaluation identifies:
- An outdated front-end framework
- Inconsistent naming conventions
- Weak automated protection round billing
- Overly broad manufacturing entry
- An untested catastrophe restoration process
- One engineer who owns most deployment information
- A database question creating latency for a reporting characteristic
- A number of growing older dependencies
- Restricted tenant-level infrastructure visibility
Which ought to Northstar repair first?
The oldest expertise?
The discovering with the biggest severity label?
The issue that builders dislike probably the most?
Not essentially.
Suppose Northstar is about to onboard its largest enterprise buyer. That buyer will use the billing workflow closely, requires robust entry controls, and expects particular availability commitments.
Abruptly, three findings turn out to be strategically necessary: manufacturing entry, billing regression danger, and restoration functionality.
The outdated front-end framework should matter. It simply is probably not the primary enterprise danger to take away.
That is the core precept of technical debt evaluation:
Technical severity and enterprise precedence are associated, however they aren’t equivalent.
How Ought to You Prioritize Technical Due Diligence Findings?
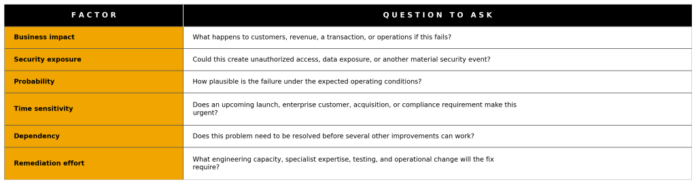
A sensible prioritization mannequin ought to think about a minimum of six components:

Don’t collapse these dimensions prematurely right into a single purple, amber, or inexperienced label.
A “medium” architectural challenge that blocks the subsequent twelve months of product improvement could deserve consideration earlier than a “excessive” discovering remoted to a not often used inner workflow.
OWASP’s Software program Part Verification Customary makes a associated level: danger acceptance can not merely be solved by way of tooling. Enterprise resolution makers want to guage controls in opposition to publicity, necessities, and constrained monetary and human sources.
The remediation roadmap due to this fact wants technical proof and enterprise context.
1. Begin With Enterprise Affect
Ask what occurs if the problem stays unresolved. Does it threaten buyer retention, block enterprise offers, delay a launch, enhance working prices, or create enterprise continuity danger?
A technically critical challenge with little enterprise publicity could not deserve the identical urgency as a smaller challenge affecting a revenue-critical workflow.
2. Consider Safety Publicity
Findings involving buyer information, extreme permissions, uncovered credentials, weak tenant isolation, or weak internet-facing programs ought to transfer increased on the listing.
Safety remediation ought to focus first on points that may realistically result in unauthorized entry, information publicity, service disruption, or regulatory penalties.
3. Assess Probability and Blast Radius
Not each weak point is equally more likely to trigger harm. Ask how simply the problem can happen and what number of customers, programs, or clients it may have an effect on.
A defect affecting one inner workflow could also be much less pressing than a shared SaaS structure weak point able to impacting each tenant.
4. Contemplate Time Sensitivity
Upcoming occasions can utterly change remediation priorities. A funding spherical, enterprise onboarding, platform launch, acquisition, or compliance overview could make sure findings pressing.
The correct remediation roadmap ought to align technical work with what the enterprise should accomplish subsequent.
5. Establish Dependencies
Some findings needs to be mounted first as a result of different enhancements rely on them. Weak testing, unreliable deployments, poor observability, or unclear entry controls could make broader modernization work considerably riskier.
Fixing these foundations first usually makes later remediation sooner, safer, and simpler to confirm.
6. Examine Remediation Effort With Threat Discount
Lastly, consider what it is going to take to resolve every challenge. Contemplate engineering effort, testing, infrastructure adjustments, specialist experience, migration complexity, and operational disruption.
Prioritize work that delivers significant danger discount, however don’t robotically keep away from troublesome fixes. A big remediation should be justified when the underlying enterprise publicity is substantial.
The aim is to not shut the best variety of findings. It’s to take away the dangers that matter most to the enterprise in the appropriate sequence.
A Sensible 30/60/90-Day Technical Due Diligence Remediation Plan
A 30/60/90-day roadmap is helpful as a result of it forces sequencing.
It’s not a promise that each technical due diligence discovering shall be mounted inside 90 days.
Massive structure migrations, safety packages, compliance initiatives, data-platform adjustments, and legacy modernization can take considerably longer. The primary 90 days ought to set up management, cut back probably the most materials exposures, and create a reputable execution path for longer-term work.
Days 0–30: Include, Validate, and Set up Management
The primary month ought to concentrate on findings that create rapid publicity and on validating assumptions behind the report.
Deal with confirmed high-impact safety exposures. Rotate compromised or unnecessarily uncovered credentials. Cut back extreme privileges. Confirm backup and restoration for important programs. Set up monitoring round materials operational dangers. Establish key-person dependencies.
On the similar time, problem unsure findings. Reproduce necessary issues the place possible. Verify which programs and buyer workflows are literally affected.
Don’t begin a six-month modernization undertaking as a result of one diagram appeared regarding throughout diligence.
By Day 30, management ought to have a validated danger register, accountable homeowners, identified rapid controls, preliminary finances ranges, and clearly recognized unknowns.
Days 31–60: Strengthen the Engineering Basis
The second part ought to cut back the situations that enable issues to recur.
Enhance automated safety round business-critical workflows. Stabilize CI/CD the place deployments are fragile. Strengthen observability. Cut back handbook working dependencies. Enhance entry administration. Doc important structure and operational procedures.
This part may additionally embody dependency upgrades or centered refactoring the place these adjustments unlock different remediation.
The aim is to extend the corporate’s capability to make subsequent adjustments safely.
For SaaS companies, consider tenant-aware operations and reliability throughout this part. AWS emphasizes that SaaS groups want visibility into tenant habits and the flexibility to reply to shifting multi-tenant workloads.
Days 61–90: Execute Structural Enhancements and Rebaseline the Roadmap
By the third part, the corporate ought to perceive the highest-risk elements of its expertise property properly sufficient to make bigger selections.
That is the place focused structure modernization, main dependency work, platform scalability enhancements, information adjustments, and technical-debt discount can start or proceed.
Don’t decide this system by what number of unique findings had been closed.
Measure whether or not significant enterprise publicity has modified.
For instance:
Has deployment failure frequency declined?
Can important providers be recovered?
Has privileged manufacturing entry been diminished?
Can the platform assist the subsequent anticipated buyer workload?
Has key-person dependency decreased?
Can engineering launch adjustments to the affected subsystem with better confidence?
At Day 90, re-score the remaining dangers primarily based on present proof and replace the longer-term software program remediation roadmap.
The report from Day 0 mustn’t turn out to be everlasting fact.
What Does a Good Technical Due Diligence Remediation Dashboard Look Like?
Don’t measure solely tickets closed.
A helpful government dashboard would possibly include:

The precise metrics ought to mirror the dangers recognized throughout the evaluation.
Don’t create a generic technical-health rating merely as a result of executives favor one quantity. A single rating can cover the distinction between a number of beauty points and one materials customer-data danger.
Actual Technical Due Diligence Ought to Inform You What Occurs Subsequent
A helpful diligence report does greater than establish flaws.
A present practitioner SaaS diligence playbook explicitly connects its findings as to whether a platform might be safely owned, assist the expansion plan, have an effect on economics, and what wants remediation after shut. Once more, it is a practitioner framework somewhat than an business normal, nevertheless it displays the business query that remediation planning must reply.
ISHIR equally describes its technical due diligence service as figuring out technical debt, estimating remediation effort, evaluating roadmap feasibility, and assessing structure, safety, scalability, documentation, engineering practices, and AI readiness.
That’s the distinction between an audit artifact and a usable expertise resolution.
A technical due diligence report tells you the place the danger is. A remediation plan tells you what to do about it with out destroying the product roadmap within the course of.
How ISHIR Helps Flip Technical Due Diligence Into an Executable Remediation Roadmap
ISHIR supplies technical due diligence for SaaS, software program platforms, cloud-native programs, enterprise expertise, and AI-enabled merchandise. The evaluation covers areas together with structure, codebase high quality, safety, scalability, technical debt, documentation, third-party dependencies, engineering practices, AI readiness, and roadmap danger.
The target shouldn’t be merely at hand management one other listing of findings. ISHIR’s technical due diligence strategy connects recognized expertise dangers with remediation effort, roadmap feasibility, value and scalability implications, and the strategic selections the group must make.
For a SaaS firm that already has a diligence report, the subsequent step might be to validate the highest-impact findings, separate rapid containment from structural remediation, estimate effort ranges, establish dependencies, set up homeowners, and outline proof for completion.
For traders and acquirers, that very same strategy will help reply one other necessary query:
How a lot extra funding will this expertise require after the transaction?
Discover ISHIR’s Technical Due Diligence Companies.
Have a technical due diligence report however no clear reply on what to repair first?
ISHIR helps flip SaaS technical dangers right into a prioritized, evidence-backed remediation roadmap aligned together with your finances and product targets.
Often Requested Questions About Technical Due Diligence Remediation
Q. What do you have to repair first after technical due diligence?
Begin with verified findings that create materials safety, buyer, income, reliability, or business-continuity publicity. Then handle foundational issues that stop secure remediation, adopted by focused technical debt and longer-term modernization. Don’t prioritize solely by the age of the expertise or the severity label within the report.
Q. How do you prioritize technical debt after a SaaS technical due diligence evaluation?
Consider technical debt in opposition to enterprise influence, safety publicity, probability, time sensitivity, roadmap dependency, and remediation effort. For SaaS merchandise, additionally think about tenant isolation and blast radius as a result of a shared architectural weak point can have an effect on a number of clients. AWS particularly identifies multi-tenant isolation, information partitioning, tenant-aware operations, and useful resource competition as necessary SaaS issues.
Q. Ought to all important technical due diligence findings be mounted instantly?
Important findings require rapid consideration, however the first motion could also be containment somewhat than everlasting remediation. Validate the discovering, perceive its publicity, introduce applicable controls, after which implement and confirm the sturdy repair. Precedence ought to mirror precise enterprise danger, not a label in isolation.
Q. How lengthy does technical due diligence remediation take?
There isn’t a accountable common timeframe. A permissions challenge could also be corrected rapidly, whereas a platform modernization or tenant-isolation redesign could require months. A 30/60/90-day remediation plan is helpful for sequencing and governance, nevertheless it shouldn’t be represented as a assure that every one materials technical debt will disappear in 90 days.
Q. Ought to technical debt be mounted earlier than new product improvement?
Not robotically. Technical debt ought to compete for funding primarily based on its impact on danger and enterprise execution. Debt that repeatedly causes incidents, prevents enterprise onboarding, will increase safety publicity, or makes roadmap supply unreliable could justify rapid funding. Low-impact debt could fairly stay within the backlog.
Q. How have you learnt whether or not technical due diligence remediation is full?
Outline verification standards earlier than implementation begins. Completion ought to imply that the unique danger has been demonstrably diminished, not merely {that a} improvement ticket was closed. Relying on the discovering, proof could embody safety retesting, restoration workouts, entry opinions, efficiency testing, deployment validation, or regression assessments.
Q. What’s technical due diligence of SaaS?
Technical due diligence of SaaS is an evidence-based evaluation of whether or not a SaaS product’s expertise can securely, reliably, and economically assist its enterprise targets. It sometimes examines structure, code high quality, safety, multi-tenancy, cloud infrastructure, scalability, technical debt, engineering practices, documentation, third-party dependencies, and operational readiness. SaaS-specific opinions ought to account for the shared and tenant-aware traits of the platform.

